When it comes to protecting ourselves against all kinds of malicious code on our computer based on the Microsoft system, we have two possibilities. On the one hand, we can use the Windows Defender antivirus, or opt for an external third-party solution.
To a large extent, this decision will depend on the tastes or preferences of the users. Each one installs on their computer what they are most interested in at the software level, although both proposals are valid. Despite the years it has been with us and the growth it has experienced, there are still many users who reject the aforementioned Windows Defender. However, something that we must take into account is that it is one of the most effective security solutions that we have at our fingertips.
In addition, it integrates seamlessly into the operating system itself, as is easy to imagine, so we will hardly notice that they are running in the background. We could say that it is a less intrusive solution than the third-party antivirus that we can install. At the same time, this solution is full of functions that little by little have been integrated into the antivirus to cover more security sections.
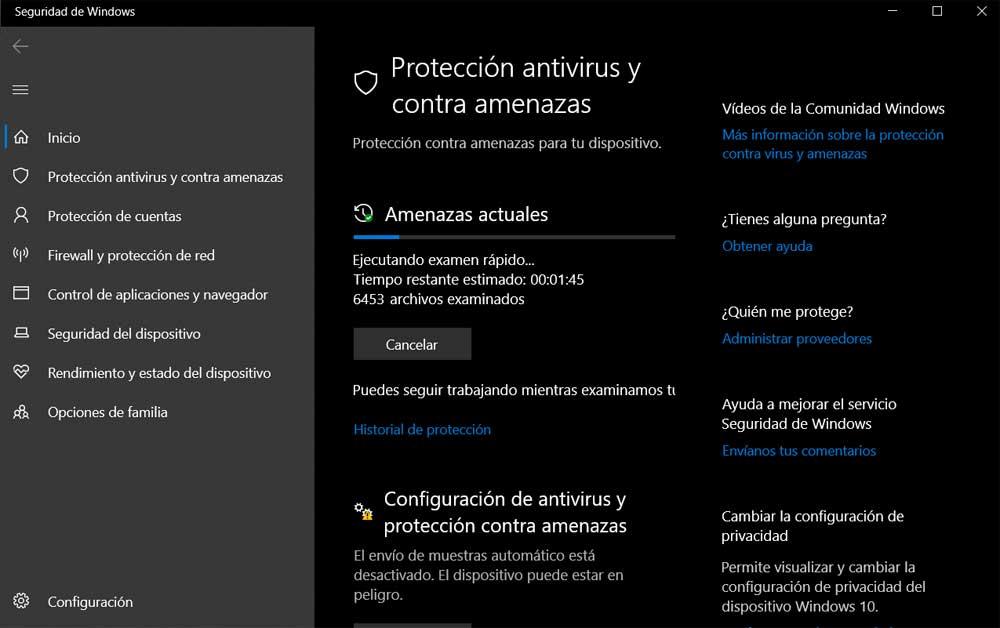
To all this we must add that we have different types of analysis against malware, all depending on the depth or scanning time that we want to use. But that’s not all, we have protection against ransomware , a firewall, application control, protection of minors, etc. But along these lines we want to focus on the behavior we must have when the software detects a threat.
Quarantine or delete, what do I do in Windows Defender
Regardless of the type of analysis we select, when Windows Defender detects a threat, it gives us the possibility of eliminating it or putting it in quarantine. In fact, this is quite common in most of the antivirus that we use today. Therefore, not at this point when the analysis has finished, we can ask ourselves what to do with the potentially malicious files detected.
The first thing to keep in mind is that antivirus programs are not 100% effective . This is something that we can attribute both to the detection of malicious elements, and to pointing out files without malware. Hence precisely the constant updates of its database, and the false positives. With this is what we want to tell you is that sometimes the antivirus can mark a file as malicious that in reality is not. This is precisely where we can take advantage of the possibility of quarantining these contents .
If you are unsure whether a detected file is safe, choose Quarantine. Defender blocks and isolates it, leaving time to investigate. Choose Remove for a threat you want deleted. Do not choose Allow on device just because you need the file.
Review the detection in Protection History
- Open Windows Security > Virus & threat protection > Protection history.
- Expand the detection and review the affected item and action taken.
- For a quarantined item, Remove deletes the threat; Restore puts the file back and Defender can detect it again.
Restore or allow a file only after establishing that it is a false positive. If uncertain, keep it quarantined, update Defender and seek the software publisher’s guidance. Microsoft’s Protection History documentation explains the alerts and actions. For broader setup checks, see what to do after a fresh Windows installation.